UK Business Continuity: Cyberattacks and Physical Emergencies
A practical UK business plan for a major cyber outage or physical emergency: protect people, keep services running, test recovery and check reporting duties.
The short answer
A widespread cyber incident and a physical emergency demand different first decisions: check life safety, confirm what is known and put a named incident lead in charge.
For a cyber disruption, assess containment and recovery with specialists; for a physical threat, follow emergency services and choose a site-specific safe response, not automatic evacuation.
UK SMEs can prepare with offline contacts, accessible site plans, tested backups and fallbacks for payroll and customers while checking reporting, pay and insurance obligations case by case.
On this page
The card terminal has stopped working. Your cloud phone system is down. A manager wants to send everyone home; another wants to pull the plug on every server. Then a message appears in the staff chat claiming that the outage is part of an attack on the UK. What do you actually know, and who decides what happens next?
A nationwide cyber disruption and a physical emergency are different problems. A company can often continue safely in a cyber outage with carefully controlled manual processes. A physical threat can make the same office unsafe even if its computers still work. Both may occur together, but neither should be treated as imminent simply because a risk register describes a possible scenario. The government's National Risk Register is for planning, not a prediction of war.
This guide is for UK owners, directors and operational leads preparing proportionate plans. It is not a substitute for emergency-service instructions, site-specific safety assessments, legal advice or specialist cyber response.
First, decide what is in danger
Protect people before systems. Check whether an IT failure has affected door access, alarms, medical devices or industrial controls. If there is immediate danger to life, use the appropriate emergency response and call 999. Otherwise establish facts through trusted channels, convene your incident lead and keep a written record. NCSC guidance for the first hours of a disruptive cyberattack calls for incident command, triage and an informed decision about isolation or shutdown.
The following decision map is qualitative guidance, not a threat forecast. It separates the trigger, first decision and operational fallback.
Systems or data are unavailable or untrusted; premises may still be safe. Check safety-critical dependencies, establish incident command, assess containment with specialists, then use verified manual services where safe.
People or the building may be at risk. Call 999, follow official directions and choose a safe site response for this hazard. Do not send people into an unsafe street simply because an alarm sounds.
Power, networks and access routes may fail together. Put life safety first. Use a paper contact tree, pre-agreed deputies and an off-site recovery location only when travel and communication are safe.
In a hybrid event the distinction still matters: a cyber responder should not order an evacuation because a dashboard is red, and a site manager should not wait for an IT investigation before moving people away from a fire. Assign separate technical and site-safety leads who share one incident log.
Before an incident: build a plan you can use offline
The aim is not to buy every resilience product. Identify the minimum services that keep people safe and the organisation solvent: contact with staff, payroll, incoming payments, customer updates and a way to serve essential clients. Write down which applications, suppliers, premises, electricity and people those services depend on. A backup of sales data is little use if no one can access the identity system required to restore it.
Name decision-makers and their deputies
Give one senior person authority to set priorities and a named deputy who can act when that person is unreachable. Include an IT or managed-service-provider contact, a premises lead, a staff-welfare contact and someone who can approve customer and regulator messages. For a small firm, one person may fill several roles; record what happens if they too are unavailable. The NCSC incident-management approach supports preparing roles and practising decisions. Gold, Silver and Bronze are useful labels for larger teams, not compulsory job titles for every SME.
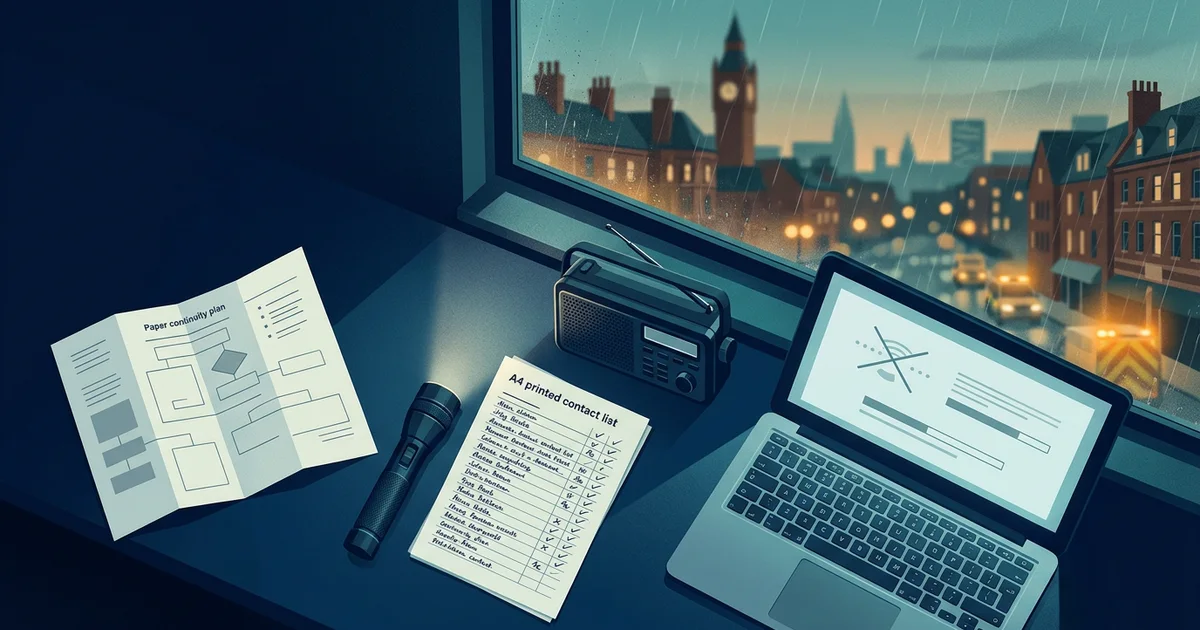
Keep a restricted paper copy of essential contacts and procedures at a safe location, plus a protected digital copy outside the potentially affected network. Handle personal contact details securely, update them, and test a second communication route. Avoid circulating a complete staff list in an unprotected group chat. Rehearse a scenario in which your normal email, cloud documents and office phone all fail.
Separate your recovery routes
Maintain backup copies protected from routine administrator access and test restoring applications and access as well as files. An offline or otherwise suitably isolated copy can reduce the chance that ransomware deletes the recovery set. Also consider whether a fire or police cordon could deny access to both the primary system and its backup. The NCSC's preparation guidance covers technical recovery capabilities; the exact arrangement should reflect the size and dependencies of the business. A second physical building is not mandatory for every firm; choose proportionate physical and digital separation.
For physical emergencies, inspect the site's exits, protected spaces, alarm methods and accessibility arrangements with the responsible premises team. An accessible response must account for staff, contractors and visitors who need assistance or cannot receive an audio-only instruction. ProtectUK's venue guidance recommends site-specific plans, trained staff, communication methods and exercises. Adapt this guidance to your premises and applicable fire-safety duties; do not copy a stadium procedure into a small office unchanged.
Find your area's resilience partnership and community risk register. They help contextualise local hazards, but a company should not presume its employees will receive direct operational orders from the forum during every event.
Test the dependencies nobody owns alone
A continuity plan that assumes broadband, power, payment processing and the main supplier will all remain available is fragile. Ask each critical provider which services rely on the same cloud platform, telecommunications route or local premises. If the answer is unknown, record that uncertainty rather than declaring the supplier resilient. Write down how to verify a supplier's status through an independent channel and who is authorised to accept a temporary substitute.
Make the exercise concrete: a distributor loses access to ordering software while the bank still works. The operations lead can record urgent orders on numbered paper forms, but only after agreeing who checks quantities and prevents duplicate fulfilment when the software returns. The finance lead must know which invoices can be paid and how to guard against a forged supplier message asking for a new bank account. A telephone confirmation using a pre-existing trusted number is more reliable than calling the number in the unexpected message.
If emergency working involves moving staff to another site, test the whole journey. Is travel permitted and safe? Can the alternate location admit people who need step-free access? Will the team be able to use a printer or private room without exposing client data? Could the manager who holds the keys also be unavailable? A plan only earns its place in the grab bag when someone other than its author can carry it out.
Scenario A: a widespread cyberattack or digital outage
An incident can originate in your own systems, a supplier, a shared software dependency or critical infrastructure. At the outset you may not know whether it is malicious, national in scale or simply a service outage. Do not announce attribution before evidence exists.
First hours: stabilise, investigate, decide
- Check physical safety. Are alarms, electronic locks, equipment or customer-facing services creating immediate harm? Switch to the relevant site-safety plan if necessary.
- Appoint an incident lead and recorder. Capture what failed, when it was first observed, who made each decision and why. Use an alternative channel if corporate email may be compromised.
- Ask the technical lead to map impact. Which systems still work? Which accounts or services might be untrusted? What do critical functions depend on? Engage an NCSC-assured incident-response provider when the incident warrants specialist help.
- Contain deliberately. Disconnecting a compromised system can limit further spread and preserve evidence; powering it down can sometimes be necessary but may erase useful evidence. Consider safety and business impact with a qualified responder. Neither ‘pull every cable’ nor ‘leave everything running’ is a universal rule.
- Communicate what is verified. Tell staff what services they must not use, what approved fallback they can use and when the next update is due. Keep customer messages factual and revise them as the investigation develops.
The NCSC's reporting route can help the organisation and national understanding, but reporting to the NCSC does not fulfil any separate regulatory notification obligation. Make the legal reporting assessment independently.
The following days: restore in the right order
Prioritise services by business need, not by which server is easiest to switch on. Confirm that backup sets and the restoration environment are trustworthy; seek specialist advice before reconnecting systems to a potentially compromised network. Rotate exposed credentials and verify the attacker's access has been contained before treating recovery as complete. NCSC recovery guidance treats investigation and recovery as linked work, not simply a restore button.
Have a low-tech fallback for orders, invoices and customer enquiries. Limit what personal information is written on paper, record who holds it, and securely reconcile and dispose of temporary records when systems return. If a fallback cannot be carried out safely or lawfully, pause that service and explain the interruption rather than improvising.
A national outage also creates a communications trap. A genuine supplier notice, a fake account claiming to be your bank and an internal rumour can arrive within minutes of one another. Nominate one person to validate status through official provider pages or previously recorded phone numbers. Date each staff update, distinguish confirmed facts from working assumptions, and publish the next update time even if you have little new information. Do not ask employees to upload sensitive incident screenshots to a public AI tool for a quick explanation. The attacker's material may be misleading and the upload may reveal company or customer data. Our guide to local and cloud AI data boundaries examines the wider handling issue; it is not a substitute for incident-response advice.
For an example of why a sudden fall in automated traffic cannot by itself establish who is behind an information campaign, see our analysis of the Yandex outage. The same evidential discipline applies when an executive wants to name a perpetrator before the investigation has identified one. If customers ask whether their data is affected, say what you know, what you are investigating and how they will receive updates; do not replace uncertainty with premature reassurance.
Scenario B: a physical attack or wartime emergency
An event elsewhere in the country does not automatically mean your building must close. Equally, a local explosion, hostile threat, fire or official cordon demands a site-specific response even if there has been no national declaration. The first question is where the danger is relative to people, exits and safe areas. Follow the emergency services and GOV.UK Emergency Alerts; verify alarming social posts before forwarding them. Alerts are not the only warning channel, so maintain a radio or other practical fallback.
Choose a safe movement response, not an automatic evacuation
ProtectUK explains why the safe action depends on the incident. Evacuation may be right for an internal hazard such as fire, provided the route moves people to safety. Invacuation moves people further inside if going outside could expose them to an external threat. Dynamic lockdown may be appropriate for a hostile intruder or immediate weapons threat, but it must be managed and reversible if fire or another hazard makes staying inside more dangerous. These are options for trained, site-specific decision-making, not instructions to shelter in a basement or seal ventilation in every incident. For a direct weapons attack, follow the relevant RUN HIDE TELL guidance.
Call 999 when appropriate and state the exact location, type of incident, hazards, safe access, casualties and services needed or already present. ProtectUK identifies this as ETHANE. Account for staff and visitors when it is safe, arrange accessible assistance, prevent others entering a dangerous site and avoid sending remote workers into a cordoned area. Don't insist that staff travel to a site merely to collect equipment.
Preserve continuity after the immediate threat
Only after safety is established should the business decide whether to relocate, work remotely or suspend a service. A cloud system may be working perfectly while employees cannot safely reach the building; conversely, a damaged office may be survivable if an alternate site and safe routes exist. Check critical suppliers, payroll and a safe way to communicate with customers. Authorise reopening based on actual premises and official information, not a rumour that the wider crisis is over.
Suppose the office is outside a police cordon, but the approach road is closed and buses are suspended. A director's first question is not ‘Which laptop can we collect?’ but ‘Who is safe, who cannot get home, and who is authorised to tell colleagues not to travel?’ The welfare lead checks in with people who were on-site, commuting or visiting; the site lead verifies access with the authorities; operations evaluates remote and alternative-site work without demanding travel into an uncertain area. If a staff member cannot be reached, follow your pre-agreed escalation procedure rather than posting their personal details publicly.
Later, reopening needs its own decision. Check the building, utilities, fire systems, access controls and supplies; confirm staff have reliable information about where and whether to report. If access remains restricted, a practical temporary service may be smaller than normal. Tell customers the service that is actually available, the next review point and how to contact a human if their need is urgent. Careful expectations are more useful than a heroic promise to resume everything tomorrow.
An accessible response timeline
These are decision phases, not a claim that any emergency follows a fixed number of hours. Work through them in order while revisiting safety as conditions change.
| Phase | Lead decision | Evidence or fallback to have ready |
|---|---|---|
| Prepare now | Director and site lead identify essential services, safe locations, deputies and staff needs. | Printed contacts, tested backup restoration, alternative communications and site-specific accessible procedures. |
| When disruption begins | Site lead checks life safety; incident lead opens a single record and distinguishes confirmed facts from reports. | Official alert or emergency-service instruction; trusted supplier status; staff check-in method. |
| Once stabilised | Technical lead assesses isolation and recovery; operations lead selects minimum viable service. | Preserved logs and backups, approved manual fallback and clear customer holding message. |
| Before reopening | Responsible leads verify premises, systems, people and suppliers can operate safely. | Safety clearance where applicable, recovery checks, reconciled records and a staff update. |
A useful rehearsal involves three surprises: the deputy cannot be reached; the cloud phone system and staff chat both fail; and one employee cannot use the usual exit. If the team cannot show who decides and how it communicates, simplify the plan and practise again. NCSC Exercise in a Box offers a practical way to test cyber decisions.
Reporting, pay and insurance: avoid blanket assumptions
A cyber incident is not automatically a reportable personal-data breach. Assess whether personal data has been compromised and the risk to people's rights and freedoms. The ICO says a controller reports a notifiable breach without undue delay and, where feasible, within 72 hours of becoming aware; a processor tells its controller without undue delay. Document breaches and decisions even when an ICO report is not required. Other sector-specific duties may apply. The proposed Cyber Security and Resilience Bill must not be treated as law already in force.
A shutdown does not automatically remove pay obligations. Acas advises that lay-offs and short-time working should be a last resort. Employees normally receive full pay unless a valid agreement or contractual provision permits otherwise; qualifying workless days may attract statutory guarantee pay. Check current rules, contracts and individual circumstances with HR or an employment specialist before announcing unpaid leave. Treat travel disruption and serious safety concerns separately from a business decision to shut a safe workplace.
Insurance depends on the actual wording and circumstances. Cyber, property and business-interruption cover can have different triggers, exclusions and notice requirements. Ask your broker now whether state-linked cyber operations, war, terrorism, denial of access and supplier outages are covered by each policy; keep the insurer informed during an incident as required. Do not promise cover on the basis of a generic policy label. Commercial force majeure clauses likewise depend on their own terms; obtain legal advice before telling customers an obligation has been cancelled.
What a small firm can do this week
- Owner: name a decision-maker and deputy; write a one-page essential-services list with the supplier and person each service needs.
- IT lead or provider: test restoring one critical service from an isolated backup; record the credentials and dependencies needed to do it again.
- Premises lead: check local fire and site-emergency arrangements with the responsible person, including accessible alerting, safe routes and a fallback if doors or power fail.
- People lead: test a secure offline contact tree, including an alternative to company email and a plan for staff who cannot travel or receive standard alerts.
- Finance and communications leads: agree how to pay staff and contact customers during a system outage, and check insurance notification requirements before a claim arises.
No drill can make every contingency predictable. It can reveal a dangerous assumption while there is still time to fix it. For related reading on evaluating cyber controls rather than relying on a single technical fix, see our UK cyber defence guide and analysis of deployment security.
Conclusion
The practical question is not whether a UK-wide attack is about to happen. It is whether your organisation can tell a digital outage from a threat to life, keep decisions and communication working without its usual systems, and recover without putting people or evidence at risk. Build a proportionate plan, test it with the people who will use it, and defer to verified emergency direction when real conditions differ from the exercise.
Key takeaways
- Protect people first: Check physical safety even during a cyber incident; follow emergency services and official alerts when there is a threat to life.
- Contain with judgement: NCSC guidance calls for assessed isolation or shutdown, not a universal instruction to turn off every system.
- Choose movement by hazard: Evacuation, invacuation and lockdown are site-specific options, not interchangeable emergency slogans.
- Test the fallback: Offline contacts, accessible site procedures and a restored critical service matter more than a plan that exists only in the cloud.
- Check legal triggers: ICO notifications, employee pay and insurance cover depend on the facts and applicable rules or policy wording.
TTAI Editorial Team
AI Research & Analysis Experts
Our team of AI specialists tests and evaluates AI agent platforms to provide UK businesses with practical guidance on digital transformation and automation.
📄 Sources & Research References (14 sources)
- [1] National Risk Register (gov.uk)
- [2] NCSC guidance for the first hours of a disruptive cyberattack (ncsc.gov.uk)
- [3] NCSC incident-management approach (ncsc.gov.uk)
- [4] NCSC's preparation guidance (ncsc.gov.uk)
- [5] ProtectUK's venue guidance (protectuk.police.uk)
- [6] Find your area's resilience partnership and community risk register (gov.uk)
- [7] reporting route (ncsc.gov.uk)
- [8] NCSC recovery guidance (ncsc.gov.uk)
- [9] GOV.UK Emergency Alerts (gov.uk)
- [10] RUN HIDE TELL guidance (protectuk.police.uk)
- [11] NCSC Exercise in a Box (ncsc.gov.uk)
- [12] ICO says (ico.org.uk)
- [13] Cyber Security and Resilience Bill (gov.uk)
- [14] Acas advises (acas.org.uk)